
TYPO3 News & Events Hub
What’s new & what’s comin’
TYPO3 CMS 6.2.29, 7.6.13 and 8.4.1 released

The TYPO3 Community announces the versions 6.2.29 LTS, 7.6.13 LTS and 8.4.1 of the TYPO3 Enterprise Content Management System.
Read moreOur Internal Workflow
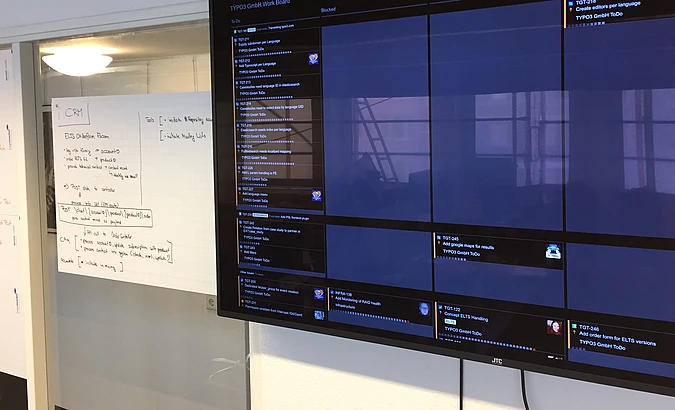

In this post we want to give you a glimpse of how we are working internally, which tools we use and what the benefits of that workflow are to us.
TYPO3-EXT-SA-2016-033: Unvalidated Redirect in extension "TC Directmail" (tcdirectmail)

It has been discovered that the extension "TC Directmail" (tcdirectmail) is susceptible to Unvalidated Redirect.
TYPO3-EXT-SA-2016-032: SQL Injection in extension "Member Infosheets" (if_membersheet)
It has been discovered that the extension "Member Infosheets" (if_membersheet) is susceptible to SQL Injection.
TYPO3-EXT-SA-2016-031: Cross Site-Scripting in extension "Secure Download Form" (rs_securedownload)
It has been discovered that the extension "Secure Download Form" (rs_securedownload) is susceptible to Cross Site-Scripting.
TYPO3-EXT-SA-2016-030: SQL Injection in extension "Shibboleth Authentication" (shibboleth_auth)
It has been discovered that the extension "Shibboleth Authentication" (shibboleth_auth) is susceptible to SQL Injection.
TYPO3-EXT-SA-2016-029: Insecure Unserialize and SQL Injection in extension "Code Highlighter" (mh_code_highlighter)
It has been discovered that the extension "Code Highlighter" (mh_code_highlighter) is susceptible to Insecure Unserialize and SQL Injection.
TYPO3-EXT-SA-2016-028: Cross-Site Scripting in extension "Store Locator" (locator)
It has been discovered that the extension "Store Locator" (locator) is susceptible to Cross-Site Scripting.
TYPO3-EXT-SA-2016-027: Cross-Site Scripting in extension "HTML5 Video Player" (html5videoplayer)
It has been discovered that the extension "HTML5 Video Player" (html5videoplayer) is susceptible to Cross-Site Scripting.
TYPO3-EXT-SA-2016-026: Multiple vulnerabilities in extension "TC Directmail " (tcdirectmail)
It has been discovered that the extension "TC Directmail " (tcdirectmail) is susceptible to Cross Site-Scripting and SQL Injection.