Relaunch Redirects Extension Finds Broken URLs Before the Go-Live
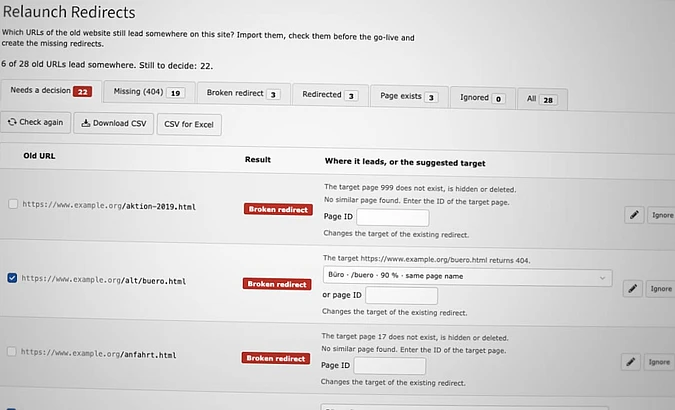

A new TYPO3 extension checks a site’s old URLs on a staging system, flags those that would end in a 404 page-not-found error, and proposes redirects. A console command can also stop a deployment when old links would fail.
Read moreTYPO3 14.3.10, 13.4.37, 12.4.51, 11.5.56 and 10.4.62 maintenance releases published


The versions 14.3.10, 13.4.37, 12.4.51, 11.5.56 and 10.4.62 of the TYPO3 Enterprise Content Management System have just been released.
TYPO3 Association Board Meeting Protocol (30 September 2026)

Proposed term limits for board and BCC members, a one-week online vote on new by-laws ahead of a short General Assembly on 29 October, and lessons from open source events in North America topped the board’s agenda.
What’s New in DDEV for TYPO3 Folks: October 2026

October’s DDEV update for TYPO3 developers is about databases: seeded snapshots, a database per branch, and faster throwaway instances. Several of the new tools come from TYPO3 community members, and the update ends with how agencies can help sustain DDEV.
TYPO3-PSA-2026-001: Critical PHP security release: PHP update required for all TYPO3 installations

Two critical security vulnerabilities in PHP require prompt action: all TYPO3 users should update PHP on their installations right away. TYPO3 itself is not affected and does not need to be updated.
TYPO3-EXT-SA-2026-036: Broken Access Control in extension "shop" (shop)

It has been discovered that the extension "TYPO3 Shop by coding.ms" (shop) is vulnerable to Broken Access Control.
TYPO3-EXT-SA-2026-035: Multiple vulnerabilities in extension "TYPO3 AI Integration Extension" (ns_t3ai)
It has been discovered that the extension “TYPO3 AI Integration Extension” (ns_t3ai) is vulnerable to SQL Injection and Sensitive Data Exposure.
TYPO3-EXT-SA-2026-034: SQL Injection in extension "File manager" (ameos_filemanager)
It has been discovered that the extension "File manager" (ameos_filemanager) is vulnerable to SQL Injection.
TYPO3-EXT-SA-2026-033: Multiple vulnerabilities in extension "TYPO3 Fluid-Form" (fluid_form)
It has been discovered that the extension "TYPO3 Fluid-Form by coding.ms" (fluid_form) is vulnerable to Cross-Site Scripting and Broken Access Control.
TYPO3-EXT-SA-2026-032: Server-Side Request Forgery in extension "Kitodo.Presentation" (dlf)
It has been discovered that the extension "Kitodo.Presentation" (dlf) is vulnerable to Server-Side Request Forgery.