

Double bug bounties for vulnerabilities in TYPO3 CMS until the end of 2024


The TYPO3 Security Team is doubling bug bounties for all verified vulnerabilities in TYPO3 CMS until December 31, 2024. This special campaign offers an opportunity for security researchers and ethical hackers to contribute to TYPO3’s security with enhanced rewards in recognition of their efforts.
Read moreTYPO3-EXT-SA-2024-007: Insecure Direct Object Reference in extension "powermail" (powermail)
It has been discovered that the extension "powermail" (powermail) is susceptible to Insecure Direct Object Reference.
TYPO3-EXT-SA-2024-006: Multiple vulnerabilities in "powermail" (powermail)
It has been discovered that the extension "powermail" (powermail) is susceptible to Insecure Direct Object Reference and Broken Access Control.
TYPO3-EXT-SA-2024-005: Multiple vulnerabilities in "Aimeos shop and e-commerce framework" (aimeos)
It has been discovered that the extension "Aimeos shop and e-commerce framework" (aimeos) is susceptible to Remote Code Execution and Insecure Direct Object Reference.
TYPO3-EXT-SA-2024-004: Broken Access Control in "Integration of Friendly Captcha" (friendlycaptcha_official)
It has been discovered that the extension "Integration of Friendly Captcha" (friendlycaptcha_official) is susceptible to Broken Access Control.
TYPO3-EXT-SA-2024-003: Multiple vulnerabilities in "Events 2" (events2)
It has been discovered that the extension "Events 2" (events2) is susceptible to Cache Poisoning, Insecure Direct Object Reference and SQL wildcard injection.
TYPO3-EXT-SA-2024-002: Authentication Bypass in "OpenID Connect Authentication" (oidc)
It has been discovered that the extension "OpenID Connect Authentication" (oidc) is susceptible to Authentication Bypass.
TYPO3-EXT-SA-2024-001: Broken Access Control in extension "Event management and registration" (sf_event_mgt)
It has been discovered that the extension "Event management and registration" (sf_event_mgt) is susceptible to Broken Access Control.
Streamlining TYPO3 Extension Visibility: TER's Packagist Integration
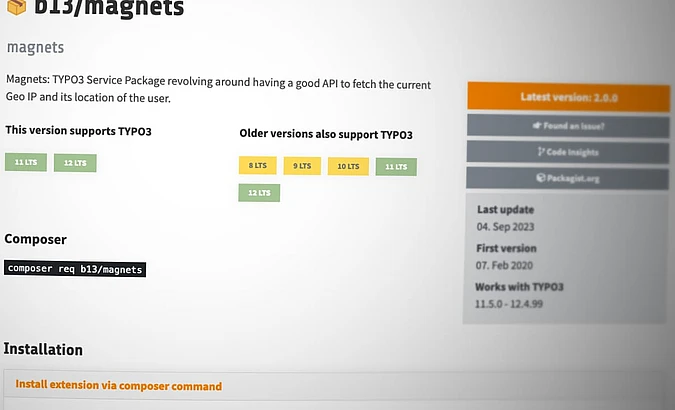
The absence of a centralized view of all available TYPO3 extensions has made it tough for users to discover extensions to meet their needs. We've long sought a solution to simplify this process. Now, TYPO3 extensions solely on Packagist are visible in the TYPO3 Extension Repository.
TYPO3-EXT-SA-2023-011: Configuration Injection in extension "Direct Mail" (direct_mail)
It has been discovered that the extension "Direct Mail" (direct_mail) is susceptible to Configuration Injection.