
TYPO3 News & Events Hub
What’s new & what’s comin’
Transparency Within, Readability Beyond: Announcing the TYPO3 Compliance Officer Mandate


Compliance doesn't have to mean bureaucracy. Rachel Foucard shares how a structural gap in the 2026 Board election became an opportunity to build something more meaningful: a dedicated framework for trust, governance, and regulatory readiness within the TYPO3 Association.
Read moreTYPO3 14.3.2 and 13.4.30 maintenance releases published

The versions 14.3.2 and 13.4.30 of the TYPO3 Enterprise Content Management System have just been released.
Bringing Fluid to VSCode
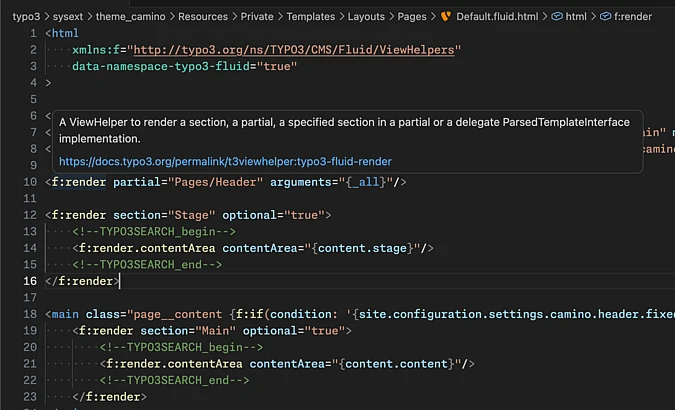

A first-party VSCode extension now provides deep integration for Fluid templates in the IDE, improving the developer experience for TYPO3 workflows.
Team Budget Report: Update the Educational Sitepackage Extension and Tutorial

This is a report about the implementation of the documentation team budget idea: Update the Sitepackage Extension and Tutorial for TYPO3 v14.
TYPO3 Education Committee Sprint, April 2026
The TYPO3 Education Committee gathered in Lübeck, Germany, for a three-day working sprint to update its certification program for TYPO3 v14. Here's a look at what the team accomplished — and what's coming in August.
TYPO3-EXT-SA-2026-013: Remote Code Execution in extension "Content Element Selector" (ceselector)

It has been discovered that the extension "Content Element Selector" (ceselector) is vulnerable to Remote Code Execution.
TYPO3-EXT-SA-2026-012: SQL Injection in extension "Address List" (tt_address)
It has been discovered that the extension "Address List" (tt_address) is vulnerable to SQL Injection.
TYPO3-EXT-SA-2026-011: Multiple vulnerabilities in extension "Faceted Search" (ke_search)
It has been discovered that the extension "Faceted Search" (ke_search) is vulnerable to XML External Entity injection, Path Traversal and Information Disclosure.
TYPO3-EXT-SA-2026-010: SQL Injection in extension "News system" (news)
It has been discovered that the extension "News system" (news) is vulnerable to SQL Injection.
TYPO3-EXT-SA-2026-009: Broken Access Control in extension "Frontend User Registration" (sf_register)
It has been discovered that the extension "Frontend User Registration" (sf_register) is vulnerable to Broken Access Control.