
Notes From the Q&A on External Mediation and Support

The online meeting answered community questions about how the new, independent external mediation service will operate. If you were unable to attend the live webinar, the full video recording is now available.
Read moreWhat Changes, What Endures: Notes From CMS Connect 2026
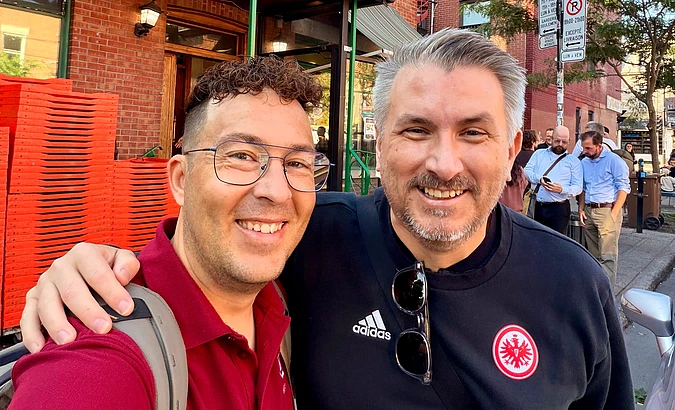

On 4–5 August 2026, I traveled to Canada to attend and speak at CMS Connect 26, an international industry conference run by Janus Boye.
TYPO3 Association Board Meeting Protocol (19 August 2026)


The TYPO3 Association Board reviewed ongoing governance and compliance work, including the Conflict of Interest Policy and preparations for the Cyber Resilience Act. The meeting also covered new community structures and potential partnerships.
TYPO3-EXT-SA-2026-027: SQL Injection in extension "Forms Export" (frp_form_answers)

It has been discovered that the extension "Forms Export" (frp_form_answers) is vulnerable to SQL Injection.
TYPO3-EXT-SA-2026-026: Broken Access Control in extension "Events 2" (events2)
It has been discovered that the extension "Events 2" (events2) is susceptible to two instances of Broken Access Control.
TYPO3-EXT-SA-2026-025: Multiple Vulnerabilities in extension "Apache Solr for TYPO3 - Enterprise Search" (solr)
It has been discovered that the extension "Apache Solr for TYPO3 - Enterprise Search" (solr) is vulnerable to Broken Access Control, Insecure Deserialization and Information Disclosure.
TYPO3-EXT-SA-2026-024: Multiple vulnerabilities in extension "femanager" (femanager)
It has been discovered that the extension "femanager" (femanager) is vulnerable to Broken Access Control and Information Disclosure.
TYPO3-EXT-SA-2026-023: Multiple vulnerabilities in extension "Event management and registration" (sf_event_mgt)
It has been discovered that the extension "Event management and registration" (sf_event_mgt) is vulnerable to Broken Access Control and Server-Side Template Injection (SSTI).
TYPO3-EXT-SA-2026-022: Server-Side Template Injection (SSTI) in extension "powermail" (powermail)
It has been discovered that the extension "powermail" (powermail) is vulnerable to Server-Side Template Injection (SSTI).
TYPO3-EXT-SA-2026-021: Broken Access Control in extension "Forum" (pforum)
It has been discovered that the extension "Forum" (pforum) is susceptible to Broken Access Control.